Skip to content
Active incident? Certified responders answer 24/7, no retainer required.  Experienced a breach? →
video poster image

Confidence has a Method.

Readiness, established. A flight plan, sequenced. | Progress, verified.


Most programs run on assumption: controls half-configured, AI nobody approved, a roadmap that was never sequenced.

We replace guesswork with clarity: a benchmark of where you stand, a prioritized roadmap for what comes next, and expert guidance every step of the way. Skyrocket Your Cyber Maturity aligns your program with the NIST CSF. Skyrocket Your AI evaluates readiness for secure AI adoption across 6 dimensions. 2 assessments. One methodology. One trusted team.

The Confidence Standard - Cybersecurity Maturity & Artificial Intelligence
Track 01 · Cyber
Track 02 · AI

How mature is your cybersecurity program?

Start here if you have tools but no clear picture of coverage, a board or audit question is coming, or your program has never been benchmarked.

Benchmarked to NIST CSF 2.0 · 4 maturity tiers · 8 weeks, weekly sessions

How ready are you to adopt AI safely?

If employees are already using AI tools, you’re being asked for an AI policy, or you’re paying for AI licenses nobody is measuring.

6 readiness dimensions · 5 tiers · Shadow AI discovery

NOT SURE WHICH ONE?

Most organizations need both eventually, the question is only which exposure is live right now.

 Take the two-minute self-assessment and we’ll tell you where to start.
2 TRACKS
One Framework, One Vocabulary
4 STAGES
From Assessment to Operation
25+ YEARS
Serving the Americas

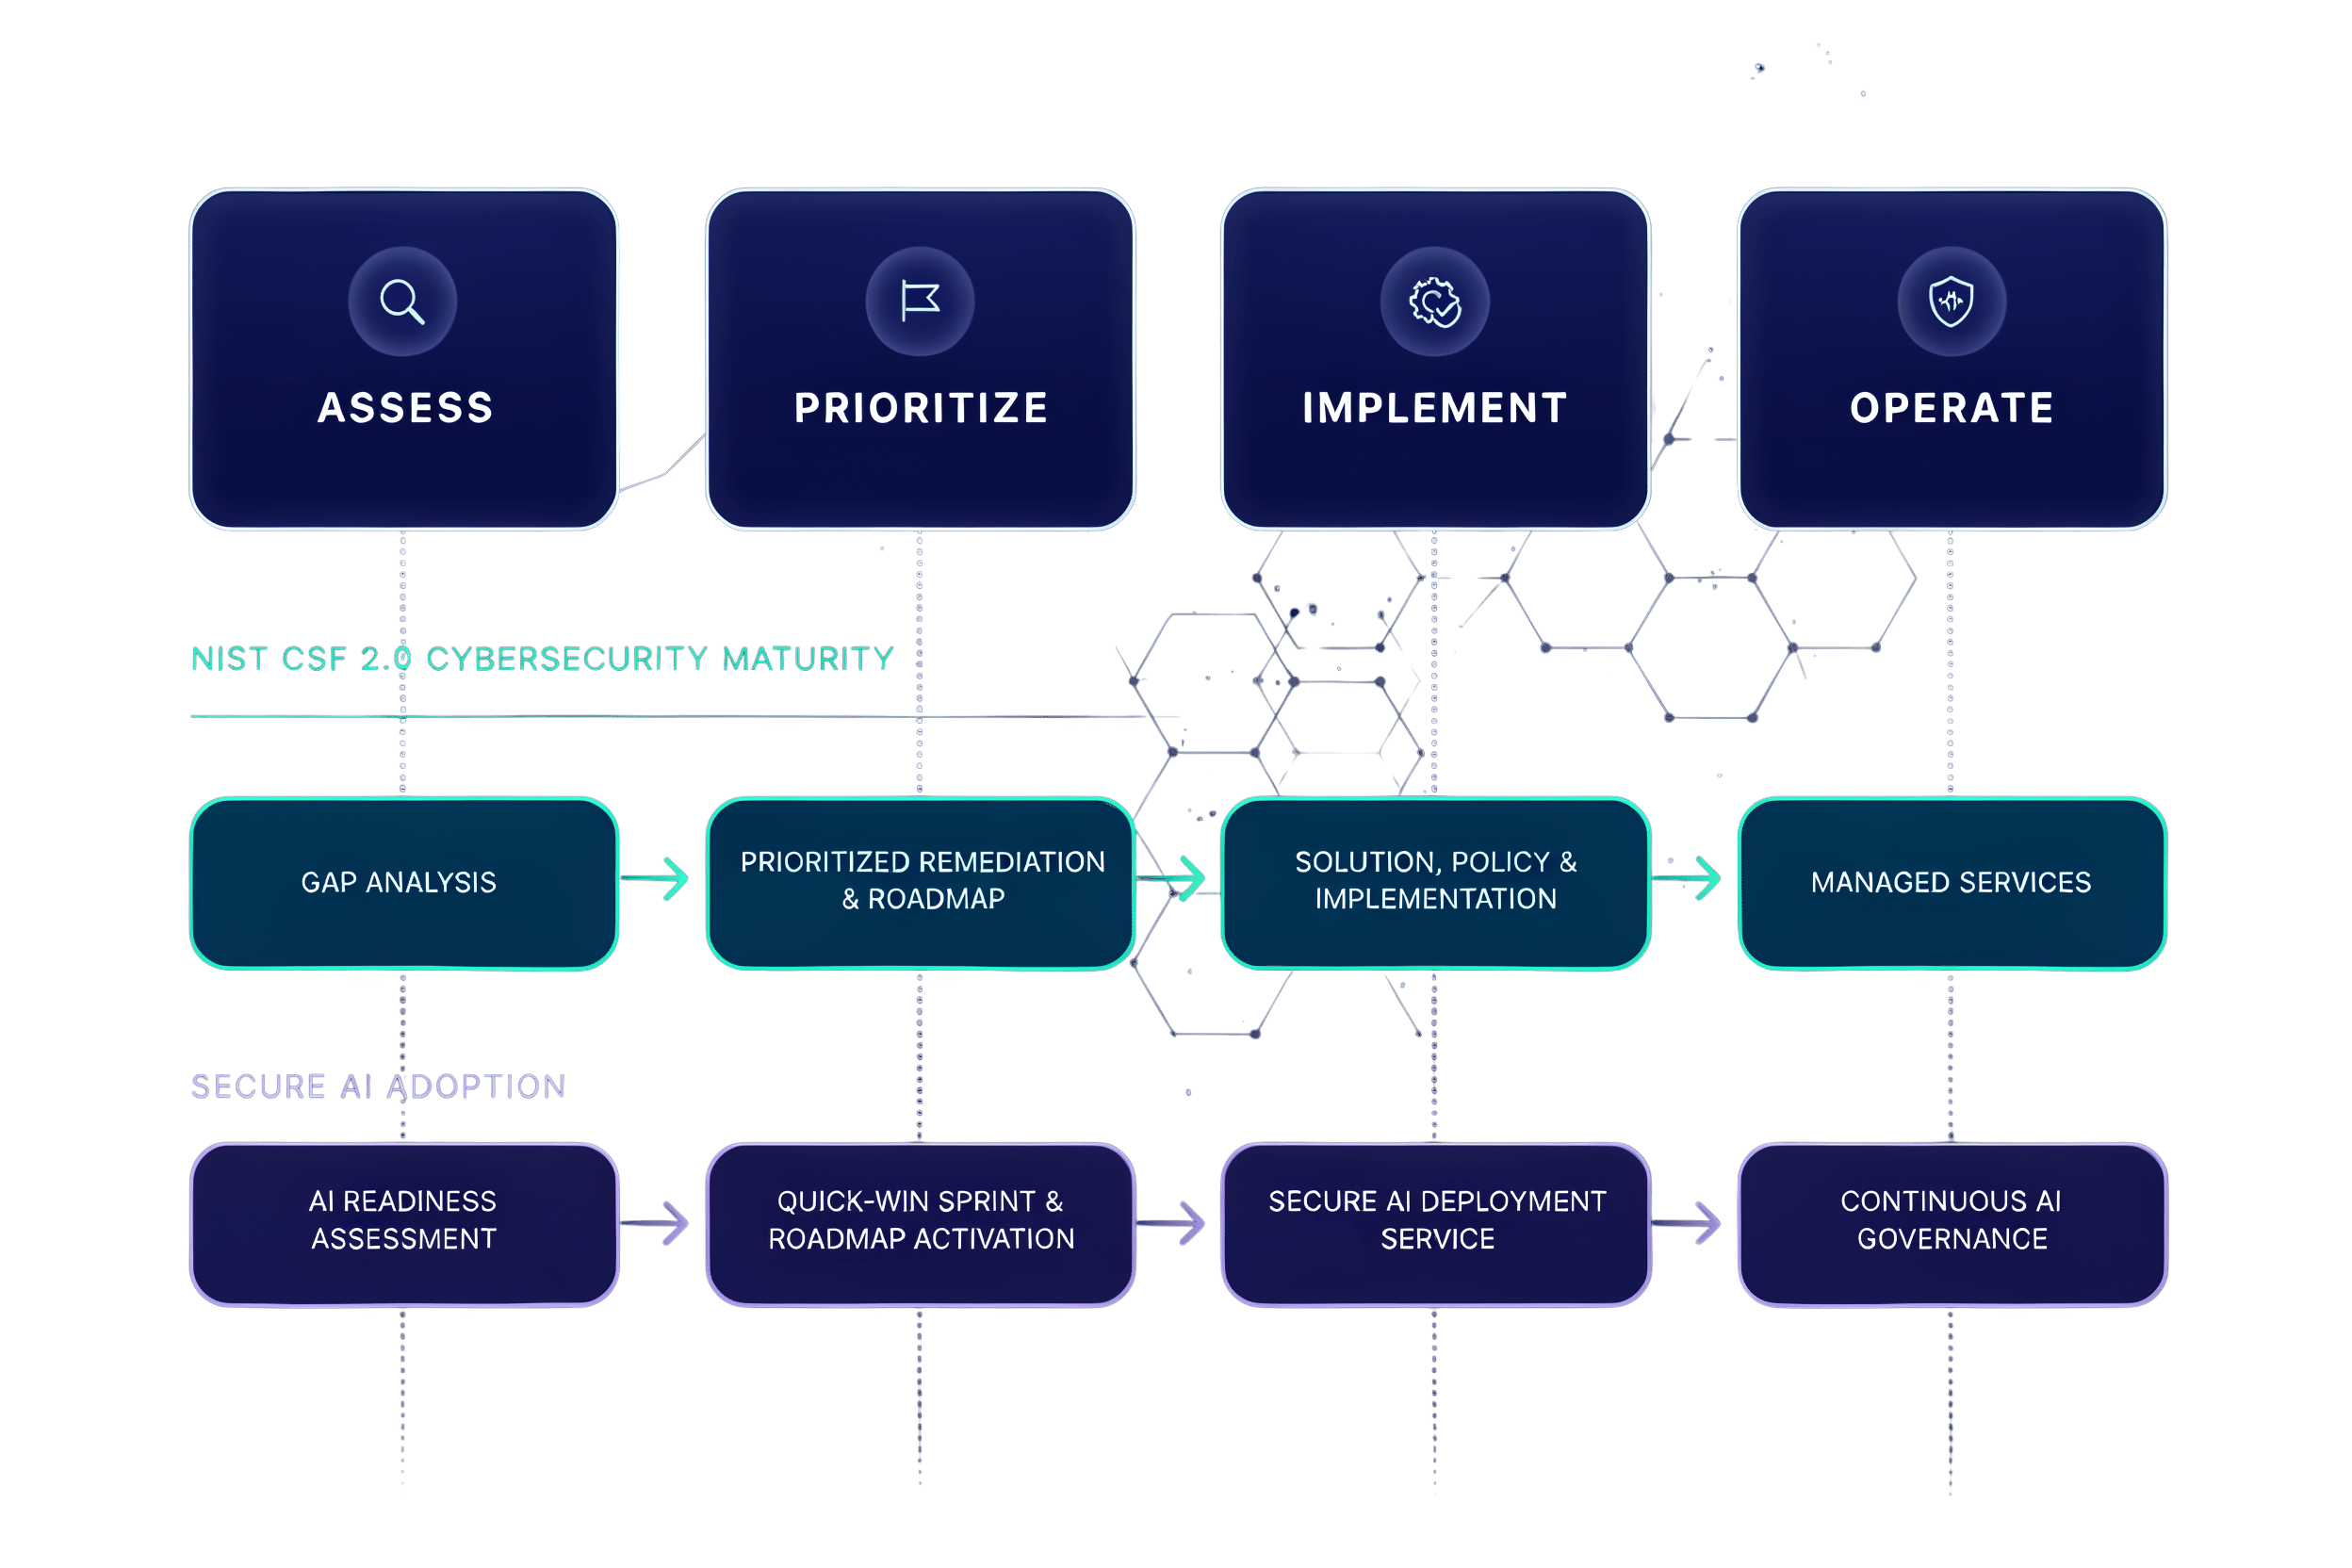
One framework. Four stages. Two tracks that run side by side.

Skyrocket is how we sequence work. Cyber and AI move through the same four stages, use the same vocabulary, and produce the same kind of flight plan. Run one, or run both in parallel, and at every stage, confidence is the thing being earned.
 

Skyrocket_diagram_2
SMALLER FRONT DOORS

Not ready for a full assessment?

Start here.

Not every conversation starts with an assessment, an active incident certainly doesn’t. Each of these is a real piece of work, and each one connects back to the same method.

Shift_SkyRocket_Guia-poster-03
{{ context.card_1_content || '

A Practical Roadmap to Strengthen Your Security Strategy

A short guide to the improvements that move maturity fastest, drawn from the engagements we've actually run. Read it before you spend another dollar on tooling.

' }}
vciso_2026_2

Strategic Cyber Leadership, at Fractional Cost

Your board wants evidence you’re managing cyber risk systematically. Our vCISO model gives you the coverage and the evidence trail without adding headcount.
N_Assessment_2026_2

See What’s Dragging Your Network Down

Step one of Visibility. A full-spectrum review of connectivity, wireless, cabling, and design, so performance issues get found before they turn into business problems.
IR_2026_2

Stop the Breach. Stabilize Fast.

Certified IR professionals for active containment and recovery, plus retainers, plan development, and tabletop exercises that make the next one survivable.
THE PORTFOLIO

Three practices. One partner. One method.

DigitalEra Group has been a cybersecurity and IT infrastructure partner since 2000, serving businesses and government agencies across the United States, Latin America, and the Caribbean from headquarters in Doral, Florida. Everything we do sits in one of 3 practices, and all three run on the same four-stage customer journey.


One door into all three. Whichever practice you need, the work is sequenced the same way — readiness established, a flight plan you can defend, progress verified. Nothing is proposed from a catalog; it is proposed against a finding.

 
FROM CODE TO CLOUD

Cybersecurity

Threats move faster than most security programs. Tools accumulate; coverage doesn’t.

We reduce risk, improve visibility, and give you the evidence to lead with confidence  across endpoint, network, cloud, identity, data, and continuous exposure management.

FROM PROVISIONING TO PERFORMANCE

IT Infrastructure

Downtime rarely announces itself. It accumulates in aging cabling, unpatched servers, and a network nobody has mapped in 3 years.

Resilient, secure, scalable environments from the edge to the core. One partner, one framework, full visibility, backed by a 24/7 NOC, with open architecture and no vendor lock-in.
 
From Policy to Model

Secure AI Adoption

AI is already inside your organization, usually ahead of your policy and your visibility.


Employees are experimenting, pilots are multiplying, and licenses you already pay for sit unused. We score your readiness across 6 dimensions, close the exposure first, and sequence adoption in the order most likely to succeed.

the evidence behind the claim

Why Organizations Partner with Us

Logo_25yrs_Mainpage
25+ Years in Market
Founded in 2000. We've worked alongside IT and security teams through four generations of technology change, and we still answer for what we build.
SOC 2 Type 2 (DEG)
SOC 2 Type II Certified
We hold our operations to the standard we assess yours against, and an independent auditor signs off on it.
 
AdobeStock_1599277562
Certified Practitioners
The credentials below belong to the people on your engagement, not a company-wide bench. Senior professionals across security, infrastructure and AI.
regional_depth
Regional Depth
Headquartered in Doral, FL., with presence in Dallas, the Dominican Republic, Puerto Rico and Trinidad. Supporting customers in English and Spanish across the whole region.
We Equip Teams Across the U.S., LATAM & Caribbean
with the Confidence to Lead, Scale & Succeed.

"We've worked with DigitalEra for the better part of a decade, and what's kept us there isn't the assessments — it's that the team who scored our environment is the same team we call at two in the morning. They rebuilt our campus network and stood up our detection program, and they've never once handed us a finding without a plan attached. When our board asks whether we're ready for what we're planning next, I can answer with evidence instead of optimism. That's what they've actually given us: the confidence to move"

A photo of Shaun Benson, Marketing Manager, Agriflora
Jane Doe
CISO, University in Florida State

regional depth

Built for the Americas

South Florida’s regulatory environment demands a different playbook than Latin America, and implementing security controls in Trinidad works differently again from Dallas. We staff, deliver, and support across all of it, in English and Spanish, with people who know the local requirements.

0 states & countries shown
DEG Offices DEG Presence DEG Customers DLX Channel Ecosystem Vendor Ecosystem

Map data © OpenStreetMap contributors · Tiles by CARTO

NEWS & PERSPECTIVE

LAtest from digitalera

Company announcements, industry recognition, and technical analysis, from the people doing the work.

answer-engine layer

Frequently Asked Questions

What does DigitalEra do?

DigitalEra Group is a cybersecurity and IT infrastructure partner founded in 2000 and headquartered in Doral, Florida. It runs 3 practices (Cybersecurity, IT Infrastructure, and Secure AI Adoption) serving businesses and government agencies across the United States, Latin America, and the Caribbean. Services span assessments, advisory, implementation, and 24/7 managed operations.

What is The Confidence Standard?

The Confidence Standard is how DigitalEra works. Every engagement begins by establishing readiness, measured against the NIST Cybersecurity Framework for security, or across 6 dimensions for AI adoption.

Findings are then explained in a live walkthrough with your leadership, sequenced into a flight plan you can defend to a board or an examiner, and verified independently as the work gets done. A named consultant owns the engagement from start to finish. Confidence has a method: readiness established, a flight plan sequenced, progress verified.

Confidence has a method: readiness established, a flight plan sequenced, progress verified.


What is Skyrocket from DigitalEra?

Skyrocket is DigitalEra Group's assessment framework, built to answer where an organization stands and what to fix first. It runs on two tracks: Skyrocket Your Cyber Maturity, benchmarked to the NIST Cybersecurity Framework, and Skyrocket Your AI, scored across six readiness dimensions.

Both produce a score, gaps ranked by risk, and a sequenced roadmap. Both follow the same four stages: Assess, Prioritize, Implement, Operate.

What do we get from a Skyrocket cyber maturity assessment?

A scored baseline of your current posture, every gap ranked by the risk it carries, and a prioritized remediation roadmap you can execute against.

Because scoring is benchmarked to the NIST Cybersecurity Framework, the result works as evidence in board reporting and audit response. Most organizations use it to redirect spending they had already planned, in a different order.

How do I know whether our cybersecurity program is mature enough?

Maturity is measurable, so score it rather than estimate it. A framework-based assessment rates your program across governance, asset visibility, protective controls, detection, and response, then positions each against a recognized benchmark such as the NIST Cybersecurity Framework.

What you want out of it is a numeric baseline and a ranked gap list, enough to defend a budget request and to sequence the next twelve months of work.


What should a cybersecurity maturity assessment actually produce?

Three things you can use: a score showing where you stand today, findings ranked by the risk each one carries, and a remediation roadmap sequenced so early fixes unblock later ones.

An assessment that ends at a findings list leaves the hardest part undone. DigitalEra's Skyrocket assessments deliver all three, benchmarked to the NIST Cybersecurity Framework so results hold up with auditors and boards.

What does Skyrocket Your AI tell us that a security assessment won't?

Skyrocket Your AI assesses AI readiness, not general security posture. DigitalEra scores 6 dimensions (Strategy & Vision, Data Foundation, Process Readiness, Technology & Infrastructure, People & Skills, and Governance, Risk & Security) into an overall AI Readiness Score, and includes shadow AI discovery and license inventory. It aligns to NIST AI RMF, ISO/IEC 42001, MITRE ATLAS, AI TRiSM, and the EU AI Act.

How do we find out which AI tools our employees are already using?

Through discovery rather than a survey.

Staff routinely use tools they haven't been asked about. Practical discovery combines network and SaaS telemetry, expense and license review, and structured interviews, which together surface both unsanctioned tools and paid licenses sitting unused.

DigitalEra includes shadow AI discovery and a license inventory in its AI readiness assessment, so exposure and wasted spend surface together.

Does DigitalEra provide ongoing managed services, or only projects?

Both. DigitalEra runs project-based professional services (assessments, advisory, implementation, incident response, and training) alongside ongoing managed services. Security managed services include MDR, XDRaaS, VMPaaS, PTaaS, SIEMaaS, and dark web monitoring. Infrastructure managed services cover networking, on-premises systems, and cloud, backed by a 24/7 NOC.


What should we do if we’re dealing with an active breach?

Call DigitalEra’s incident response line at 1-786-621-8600. Certified incident response professionals handle containment, stabilization, and recovery for active incidents. DigitalEra also offers IR retainers, incident response plan development, and tabletop exercises for organizations that want to be prepared before an incident occurs.

2 minutes - no email to start

Two minutes to a starting point.

Pick the track that matches what’s live right now. A few questions, an indicative score, and a straight answer about what to do next,  whether that’s reading a sample report or talking to someone. This is where knowing begins; the method takes it from there.


Track 01 · Cyber
Track 02 · AI

How mature is our cyber program?

How ready are we to adopt AI safely?

Indicative only. Your answers stay on this page until you choose to see your result — we ask for an email at the end, not the beginning.

 
empowering confidence

Or skip the diagnostic and just talk to us.

Some problems don’t need a score first. If you already know what you need (an incident handled, a network assessed, a policy written) tell us which practice and we’ll scope the right starting point.

prefer email?